Electronic Voting System Integrity

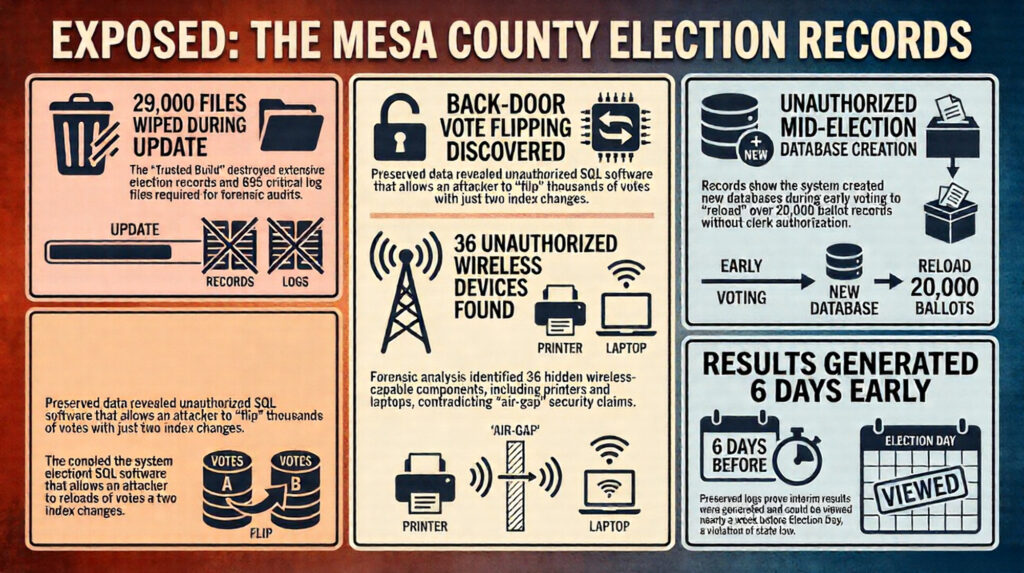
Mesa County, CO Election System Discoveries Made Possible by Tina Peters

Established Fact Tina Peters is the former Mesa County, CO clerk who was sentenced to nine years in prison for making forensic copies of her Dominion Election Management System (EMS) server in the wake of the 2020 election cycle.  In so doing, Tina prevented the destruction of election records for both the 2020 and 2021

Mesa County, CO Election System Discoveries Made Possible by Tina Peters Read More »

Election Machines Accessed the Internet (AZ)

Established Fact In the Sept. 24 hearing, CyFIR revealed and showed that not only can these ballot machines access the internet, but in Maricopa County they did access the internet. In the hearing, CyFIR provided the time & date stamps to prove it as well as the IP addresses of the computers they connected to.

Election Machines Accessed the Internet (AZ) Read More »

CISA TLP-AMBER Report: 319 Critical Vulnerabilities – 47% Active Exploitation Rate – Iranian APT Obtained U.S. Voter Registration Data – “Most Secure” Declaration Contradicts Classified Data (US)

Established Fact CISA’s own classified TLP-AMBER Election Infrastructure Subsector Cyber Risk Summary – produced but not publicly released in a voter-accessible form – documented: (1) 319 Critical-severity and 1,820 High-severity vulnerabilities in election infrastructure during the 12 months preceding Election Day; and (2) approximately 47% of election infrastructure entities with Critical vulnerabilities experienced active exploitation

CISA TLP-AMBER Report: 319 Critical Vulnerabilities – 47% Active Exploitation Rate – Iranian APT Obtained U.S. Voter Registration Data – “Most Secure” Declaration Contradicts Classified Data (US) Read More »

ESS DS400 Tabulators Equipped with Active Verizon Cellular Modems Configured to Transmit Results to Private Network IP Address (MI)

Established Fact Forensic examination of ESS DS400 tabulator thumb drives confirmed that each DS400 was equipped with a Verizon cellular wireless communications card that was active on power-up. Both devices were configured to transmit election results to IP address 10.48.51.1 – a private network address accessible remotely only through the public internet or a VPN.

ESS DS400 Tabulators Equipped with Active Verizon Cellular Modems Configured to Transmit Results to Private Network IP Address (MI) Read More »

October 23, 2020 Remote Takeover and Deletion of Absentee Ballot Processing Computer – No Criminal Referral (GA)

Established Fact On October 23, 2020 – 11 days before Election Day – a poll worker at the North Fulton Government Service Center reported that one of the computers used for Absentee Ballot Processing had been remotely accessed from somewhere else, with the remote party taking control of the computer and deleting information. This incident

October 23, 2020 Remote Takeover and Deletion of Absentee Ballot Processing Computer – No Criminal Referral (GA) Read More »

DS200 Components that Enable Hidden Remote Access Are Funded by China (US)

Established Fact President and CEO of Election Systems & Software — testified under oath. When asked about supply chain components from China or Russia, Burt stated: “We do have a limited number of components that come from China… the potential for a backdoor threat really doesn’t pertain to inert items like a piece of plastic

DS200 Components that Enable Hidden Remote Access Are Funded by China (US) Read More »

ESS Concealed pcAnywhere Remote-Access Software Installation – Installed During Period of Source Code Theft (PA)

Established Fact Election Systems & Software (ESS), which operates the largest installed base of voting machines in the United States, admitted in a 2018 letter to Senator Ron Wyden that between 2000 and 2006, it installed pcAnywhere remote-access software on election management systems sold to customers – directly contradicting prior public representations. Critically, Symantec’s pcAnywhere

ESS Concealed pcAnywhere Remote-Access Software Installation – Installed During Period of Source Code Theft (PA) Read More »

Albert Sensors / CIS Endpoint Access – Federal Monitoring of Election Infrastructure (US)

Established Fact The Center for Internet Security (CIS), recognized by DHS as the MS-ISAC and EI-ISAC, deployed Albert Sensors into local election networks nationwide under the guise of threat monitoring. These sensors actively monitor and transmit election network traffic to centralized cloud servers (AWS), introducing internet-based monitoring that bypasses local air gaps. A June 23,

Albert Sensors / CIS Endpoint Access – Federal Monitoring of Election Infrastructure (US) Read More »

ESS pcAnywhere Remote Access Software Installed on EMS Systems (US)

Established Fact Election Systems & Software (ESS) admitted in a 2018 letter to Sen. Ron Wyden that it had installed pcAnywhere remote access software on election management systems sold to customers between 2000 and 2006, directly contradicting its prior public representations that it had never done so. ESS refused to disclose which states and counties

ESS pcAnywhere Remote Access Software Installed on EMS Systems (US) Read More »

ESS Tabulators with 4G Modems; Hidden Wi-Fi at Central Count (WI)

Established Fact The Wisconsin OSC (Gableman) Special Counsel Report documented that ESS voting tabulators deployed statewide were equipped with active 4G wireless modems enabling internet connectivity. In Green Bay, all ESS voting machines were connected to a secret, hidden Wi-Fi access point located at the Grand Hyatt hotel – the central count facility – controlled

ESS Tabulators with 4G Modems; Hidden Wi-Fi at Central Count (WI) Read More »